


Global Sales of Professional Service Robots Surge 24%
7,000 Humanoids emerge as new market 117,000 Transport and logistics’ robots lead as top application Global shipments of professional service robots increased by 24% to almost 250,000 units in 2025, highlighting a successful shift tocommercial automation. These findings are presented in the World Robotics 2026 Service Robots report by the International Federation of Robotics (IFR). “Service robots are expanding into everyday operations,” says Jane Heffner, President of the In


Huawei and Qualcomm Announce Broad Patent License Agreement
Huawei and Qualcomm announced on October 5 a multi-year, broad patent license agreement that includes cross licenses to the companies’ patent portfolios across a range of technology fields, including 5G, compute, AI, and networking, together with Qualcomm’s purchase of certain Huawei U.S. patents in the areas of compute, AI, networking, and other technologies. This transaction will close following receipt of the necessary regulatory approvals. The agreement reflects the compa


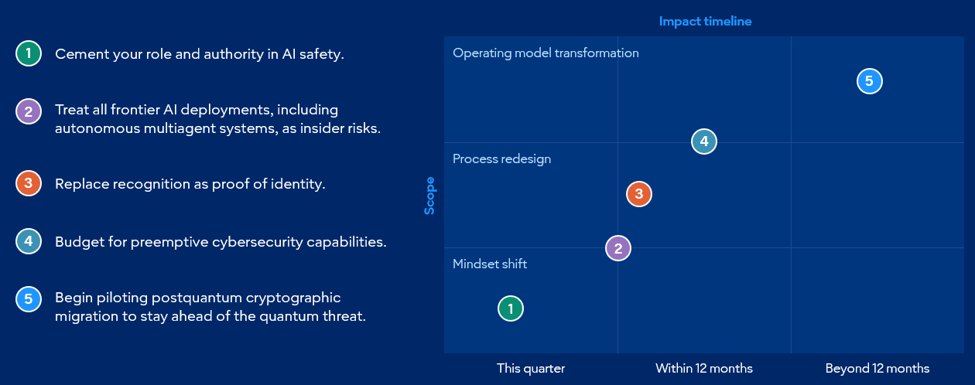
Gartner Identifies Top Five Actions for CISOs to Take by End of 2026
Cybersecurity Leaders Are Uniquely Positioned to Shape C-Suite and Board Strategy Gartner, Inc., a business and technology insights company identified five actions that chief information security officers (CISOs) should take by the end of 2026 to combat accelerating technological disruption. “AI-augmented cyberattacks, AI safety debates and emerging quantum computing risks create persistent uncertainty across the enterprise,” said Christopher Mixter, VP Analyst at Gartner. “C


DBS Gathers Global Leaders At Inaugural Asia Future Forward Conference As AI Rewrites The World
Shou Chew, Lip-Bu Tan, Hock Tan and Jenny Johnson among influential figures examining the forces reshaping business, investment and growth Some 700 senior business leaders, entrepreneurs and investors expected at DBS' new flagship conference DBS announced on October 2 the launch of the DBS Asia Future Forward Conference, a new flagship conference that will bring together global leaders in technology, business and investment to examine the forces shaping the region's future. T


IAB Hong Kong's C26 Returns as Hong Kong's Largest AI and Marketing Event, Exploring How AI Is Reimagining Business
Flagship conference by IAB Hong Kong to bring together 50+ global and regional leaders exploring how AI is reshaping marketing, media, commerce and customer engagement Artificial intelligence is moving from experimentation to scaled execution across the global marketing industry. According to IAB's 2026 Outlook Study, five of the top six marketer focus areas in 2026 are AI-driven, reflecting how rapidly AI is becoming core infrastructure for marketing strategy and business gr


Asia/Pacific AI and GenAI Spending to Reach $555 Billion by 2030 as Enterprises Scale AI Beyond Pilots: IDC
According to IDC’s Worldwide AI and Generative AI Spending Guide, V2 2026, August, Asia/Pacific AI and GenAI investment, including China and Japan, is set to grow from $121.5 billion in 2025 to $555.2 billion by 2030, a compound annual growth rate (CAGR) of 35.5%. This growth reflects enterprises moving generative AI and Agents beyond isolated pilots and into core, enterprise-wide operations. Agentic AI and orchestration platforms emerge as key catalysts, enabling enterprise


Gartner Identifies 12 Audit Plan Hot Spots for 2027
AI Value, Strains on Tech Governance and Global Fragmentation Will Shape Audit Plans in 2027 Analysts Share Latest Findings During the Gartner Enterprise Risk, Audit & Compliance Conference in London Internal audit leaders should consider 12 areas of accelerating risk exposures as they develop their 2027 audit plans, according to Gartner, Inc., a business and technology insights company. Speaking at the Gartner Enterprise Risk, Audit & Compliance Conference 2026 taking place


Citi Engages Future Leaders Through Mastercard AI Digital Safari Program in New York
In a first-of-its-kind collaboration, Citi joined forces with Mastercard to host Mastercard AI Digital Safari in New York this month, expanding the bank’s commitment to developing future leaders. Designed for the next generation of the bank’s high-net-worth wealth clients, the inaugural program brought together select participants for an immersive experience at the forefront of digital innovation. The collaboration built on the success of Citi’s Young Successor Program held i





Comments